EC-Council CEH v13 Badge Certified Ethical Hacker (CEH v13) • EC-Council Verified

Hi There! I'm

Pratik Khairnar

Certified Ethical Hacker (CEH v13) & Associate Penetration Tester based in Pune, India. Specializing in manual Web VAPT, API security (OWASP API Top 10 • BOLA / IDOR), and vulnerability assessments aligned with OWASP WSTG v4.2, ASVS, and CVSS v3.1 reporting standards.

Web VAPT
API Security
Blind SQLi
DOM XSS
OSINT Recon

Manual Web Application VAPT

In-depth manual penetration testing benchmarked against OWASP Top 10 (2021) and WSTG v4.2. Specializing in high-impact business logic bypasses, broken access control (BOLA/IDOR), multi-tenant privilege escalation, and defensible CVSS v3.1 scoring.

OWASP Top 10 (2021) OWASP WSTG v4.2 Broken Access Control BOLA / IDOR CVSS v3.1 Scoring Burp Suite Pro
Industry Credentials & Certifications

Internationally accredited offensive security and network engineering credentials verified by EC-Council and Cisco Networking Academy.

EC-Council Certified Ethical Hacker (CEH v13) Official Badge
VERIFIED CREDENTIAL
EC-Council Official Certification ANSI 17024 Accredited

Certified Ethical Hacker (CEH v13)

Validated mastery in offensive security, practical penetration testing methodologies, vulnerability assessment, and threat vector analysis. Evaluated across 20 comprehensive security domains including Web Application Security (OWASP), System Hacking, Cryptography, Network Defense, and Malware Analysis.

Issuing Body: EC-Council
Curriculum: CEH v13 (AI-Augmented Ethical Hacking)
Verification: Authenticated & Transcripts On-File
Core Focus: Web VAPT • Network Security • Forensics
Download Badge View Competencies
Cisco CCNA (Routing & Switching)
Cisco Networking Academy
VERIFIED

Enterprise network architecture, IPv4/IPv6 subnetting, TCP/IP handshake mechanics, packet inspection, VLAN segmentation, and access control list (ACL) configurations essential for high-precision network penetration testing.

B.Tech — Cyber Security & Forensics
Sandip University, Nashik • CGPA: 7.42/10
DEGREE
  • Academic Specialization — 4-Year B.Tech in Cyber Security & Forensics (Sandip University, 2023–2027).
  • Montoya Tool Architecture — Engineered AUTHENTIX Enterprise using native Java 17/21 for automated BOLA/IDOR auditing.
  • Statistical Blind SQLi Engine — Developed BlindStrike v7.0.0 in Python 3 using Interquartile Range (IQR) noise filtration.
  • Evidentiary Forensics Standards — ISO/IEC 27037 chain-of-custody protocols executed in 15+ live cybercrime investigations.
Academic Transcripts verified • Grounded in defensive & offensive systems engineering.

About Me

Certified Ethical Hacker delivering manual web penetration testing, authorization flaw verification, and offensive security engineering.

Professional Summary

I am a Certified Ethical Hacker (CEH v13) pursuing my B.Tech in Cyber Security & Forensics (2023–2027) at Sandip University, Nashik. My core operational focus is on manual web application penetration testing (Web VAPT), deep authorization flaw verification (IDOR / BOLA), and custom offensive security extension architecture.

Backed by operational experience investigating live cybercrime cases at the Cyber Police Station, Nashik Police Commissionerate and architecting custom offensive security tooling (AUTHENTIX Enterprise, BlindStrike), I specialize in identifying high-severity business logic flaws, authentication bypasses, and injection vectors beyond conventional automated scanners. Every assessment strictly adheres to OWASP Top 10, OWASP WSTG, and ASVS methodologies, delivering defensible CVSS v3.1-scored reports with verified Proof-of-Concepts (PoCs) and actionable, developer-ready remediation guidance.


Testing Methodologies & Standards
  • Manual Web Application VAPT:
    In-depth evaluations governed by OWASP Top 10 (2021) and OWASP WSTG v4.2, targeting business logic flaws, multi-tenant isolation, and privilege escalation.
  • API Security (OWASP API Top 10):
    Verification of REST & GraphQL endpoints via Postman & Burp Suite, uncovering Broken Object Level Authorization (BOLA/IDOR), JWT flaws, and OAuth 2.0 bypasses.
  • Injection & State Exploits:
    Precision verification of SQLi/Blind SQLi, context-aware DOM/Reflected XSS, SSRF, and CORS origin reflections with zero false-positive PoC validation.
  • OWASP ASVS & SANS Top 25:
    Testing benchmarked against Application Security Verification Standard (ASVS v4.0) verification levels and SANS Top 25 dangerous error categories.
Deliverables, Tooling & Compliance
  • CVSS v3.1 Scoring & Reporting:
    Production-grade VAPT reports featuring executive summaries, technical impact calculations, and standardized CVSS vector strings.
  • Remediation Roadmaps & Retesting:
    Actionable code-level mitigation blueprints, architectural fixes, and formal closure retesting validation for engineering teams.
  • Offensive Tooling & Automation:
    Custom automation with Python 3, Bash, and Burp Suite Extensions for scalable reconnaissance and high-precision exploit verification.
  • Enterprise Compliance Awareness:
    Operational alignment with industry compliance frameworks including PCI-DSS v4.0 (Req 6 & 11), ISO/IEC 27001, and NIST SP 800-115.

My Skills

Offensive security proficiencies across web application penetration testing, custom extension engineering, and digital forensics.

Web Application VAPT

OWASP Top 10 (2021) Broken Access Control (IDOR / BOLA) SQL Injection (SQLi / Blind) Cross-Site Scripting (Reflected & DOM) Server-Side Request Forgery (SSRF) Business Logic Flaw Analysis

API & Authentication Security

OWASP API Security Top 10 (2023) REST & GraphQL API Testing Postman API Test Suites JWT Token Security & Validation OAuth 2.0 & Session Management CORS & Security Headers Audit

Vulnerability Assessment & Reporting

CVSS v3.1 Severity Scoring OWASP WSTG v4.2 & ASVS v4.0 Executive & Technical VAPT Reports Remediation Consulting Retesting & Closure Verification PCI-DSS & ISO 27001 Awareness

Network Pentesting & Recon

Nmap Port & Service Scanning Wireshark Packet Analysis OSINT Attack Surface Mapping Subdomain & Asset Enumeration NIST SP 800-115 Methodologies Network Vulnerability Scanning

Security Tooling & Scripting

Burp Suite Professional Python 3 Exploit Scripting Linux / Bash Shell Automation SQLMap Database Extraction Burp Extension Engineering Git & DevSecOps Fundamentals

Digital Forensics & Incident Triage

Evidence Chain of Custody Protocols CDR / IPDR Telecom Forensics Android APK Malware Triage IOC Extraction & Attribution Network Traffic PCAP Forensics CERT-In Guidelines Compliance

Offensive Console

Interactive terminal simulating real-time VAPT workflows, reconnaissance modules, authorization testing, and credentials verification.

pratik@sec:~ (CEH v13 Offensive Shell)
Quick Exec:
[+] Pratik Khairnar Offensive Security Workstation v2.1.0
[+] CEH v13 Certified • Web VAPT Engineer • Pune, India
[i] Type help for command list, or click any quick command above. Tab completion & ↑/↓ history enabled.
pratik@sec:~$ 

My Projects

Core production security tools, frameworks, and extensions developed and maintained by Pratik Khairnar.

AUTHENTIX Enterprise
Burp Suite Montoya 34 Invariants 3-Way Diff IDOR 16 ATO Chains
AUTHENTIX Enterprise v3.0.0

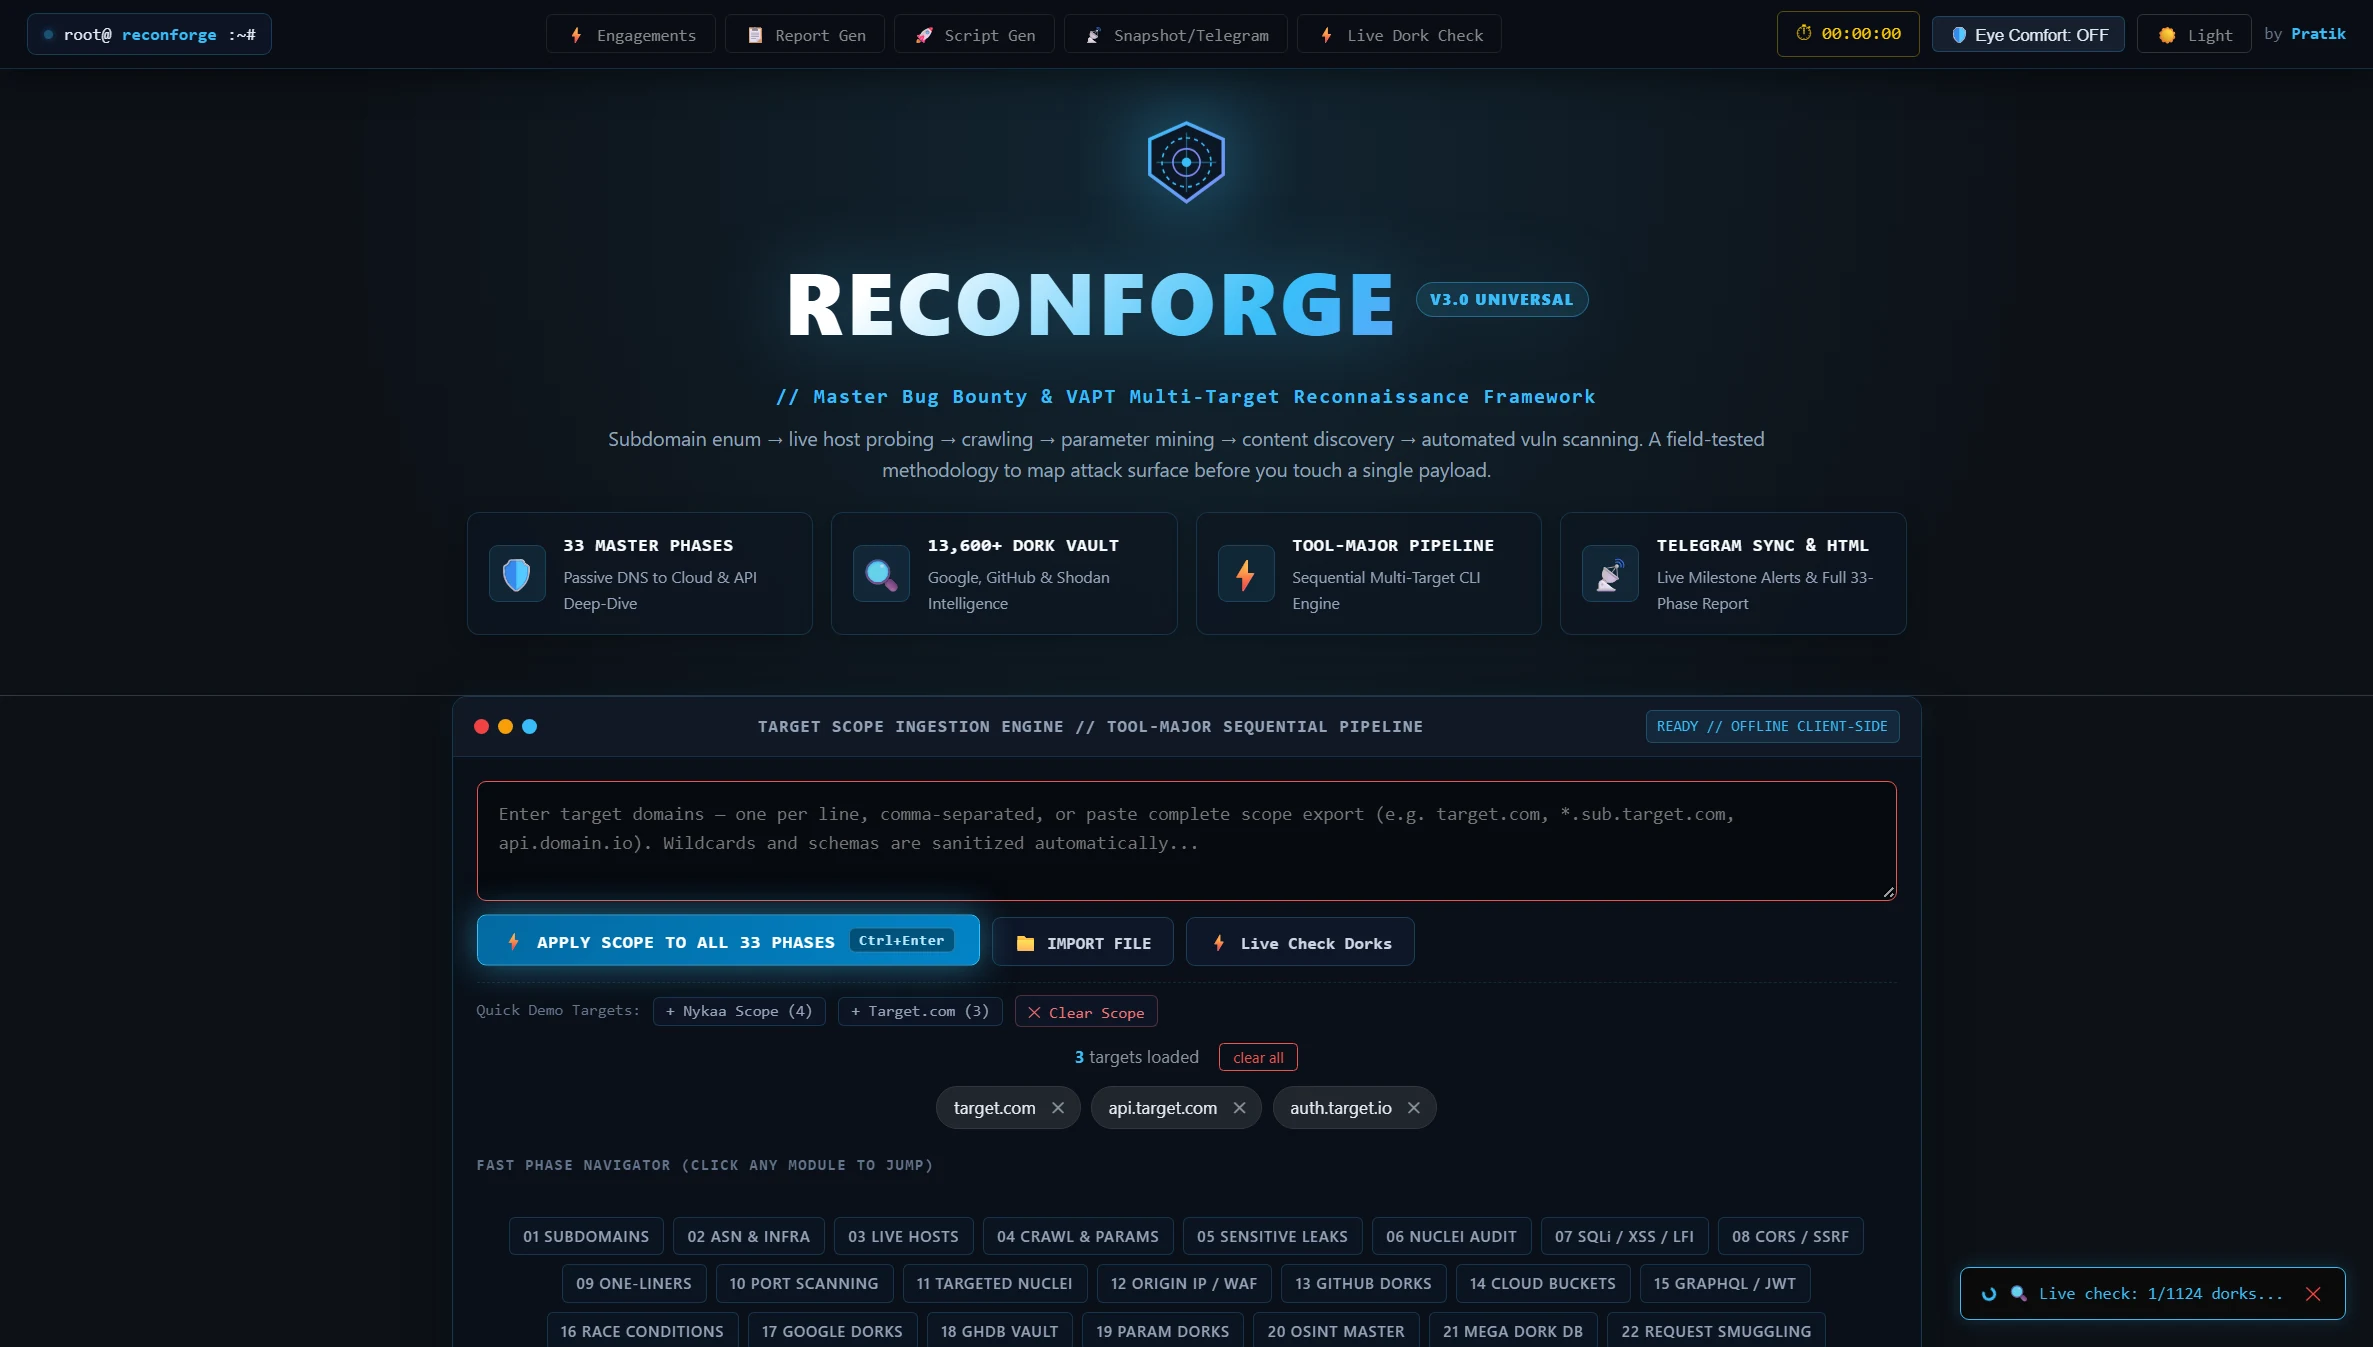
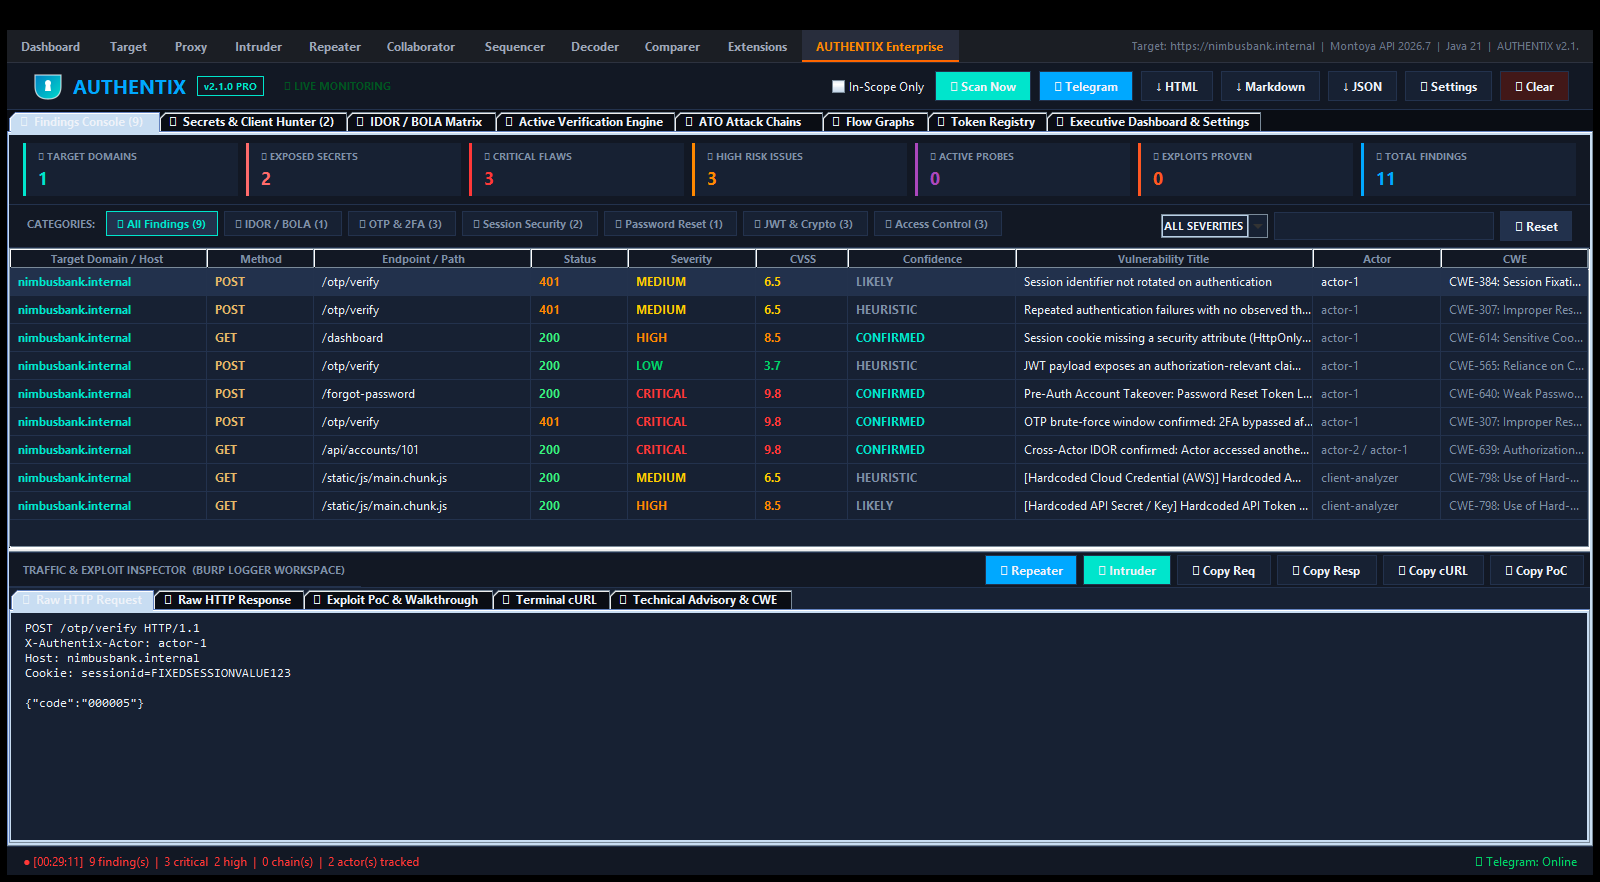
Native Burp Suite Montoya extension with 34 deterministic security invariants, 3-Way Differential IDOR Engine with Soft-200 Error Disambiguation, 16 compound ATO chains, FlatLaf Darcula UI, and 14,880 req/sec throughput.

ReconForge v4
52.6k+ Dorks 30 Phases OSINT Recon
ReconForge v4

Multi-target Bug Bounty reconnaissance framework with 30 Master Phases, 52,630+ Universal Dork Vault, and tool-major CLI generator executing 100% offline client-side.

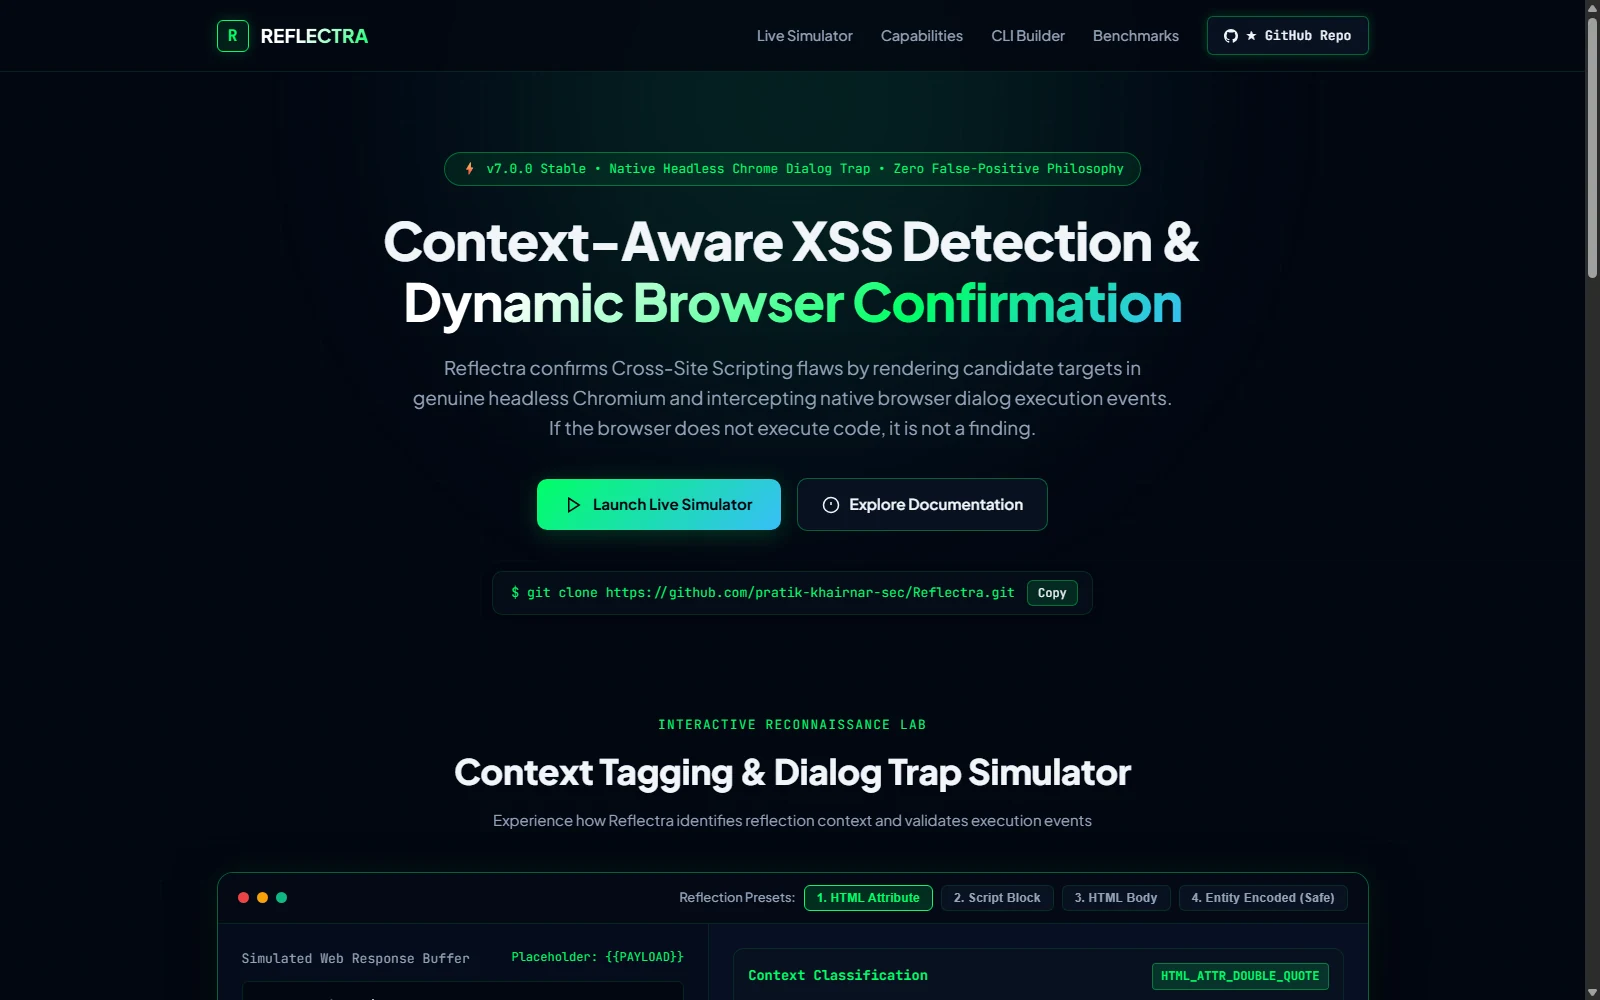
Reflectra v7
DOM XSS Python 3 Headless Chrome
Reflectra v7.0.0

Context-aware XSS scanner confirming execution via real Headless Chrome dialog evaluation with 2,600+ context-prioritized payloads and zero false positives.

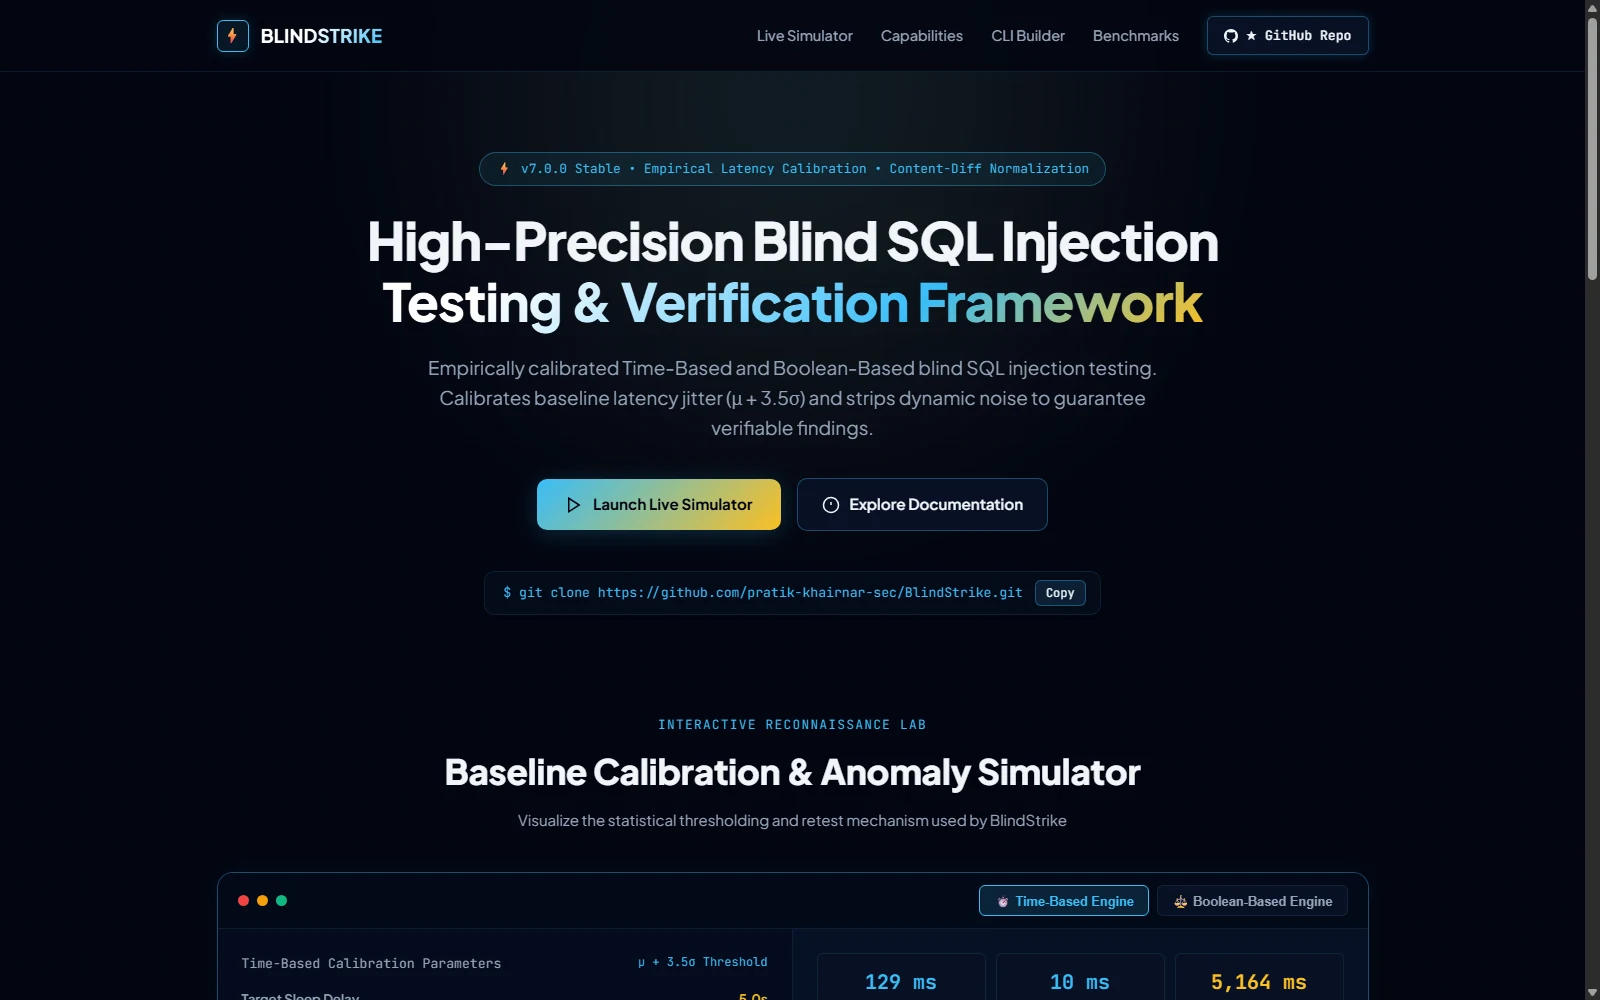
BlindStrike v7
Blind SQLi IQR Baseline Multi-DB
BlindStrike v7.0.0

Time-Based & Boolean Blind SQL Injection framework with empirical latency baseline measurement, statistical IQR jitter filtering, and multi-threaded extraction.

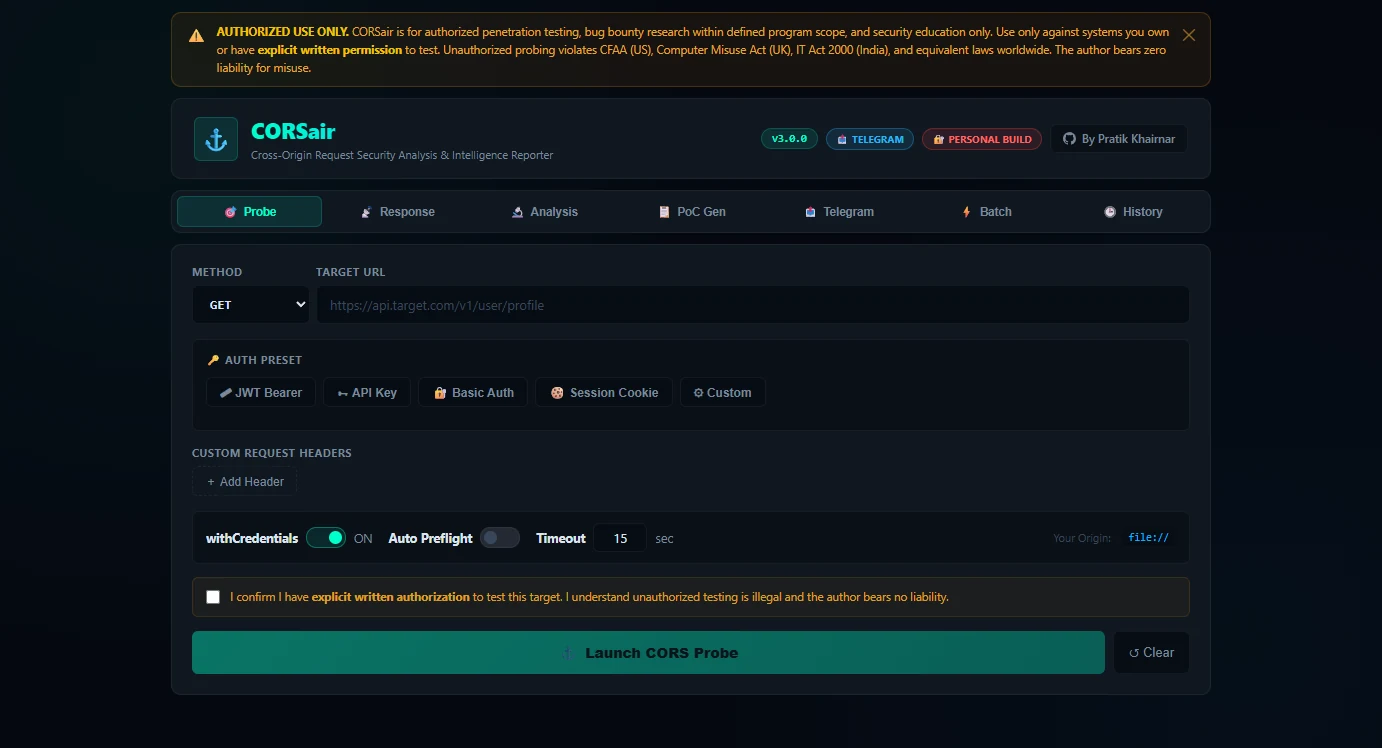
CORSair v3
CORS Auditor Shannon Entropy PoC Suite
CORSair v3.0.0

In-browser CORS misconfiguration testing tool with dynamic origin reflection verification (ACAC/ACAO), Shannon entropy token leakage calculations, and automated PoC generation.

WaybackLens
Chrome Ext (MV3) Wayback CDX Risk Ranking
WaybackLens v1.0.0

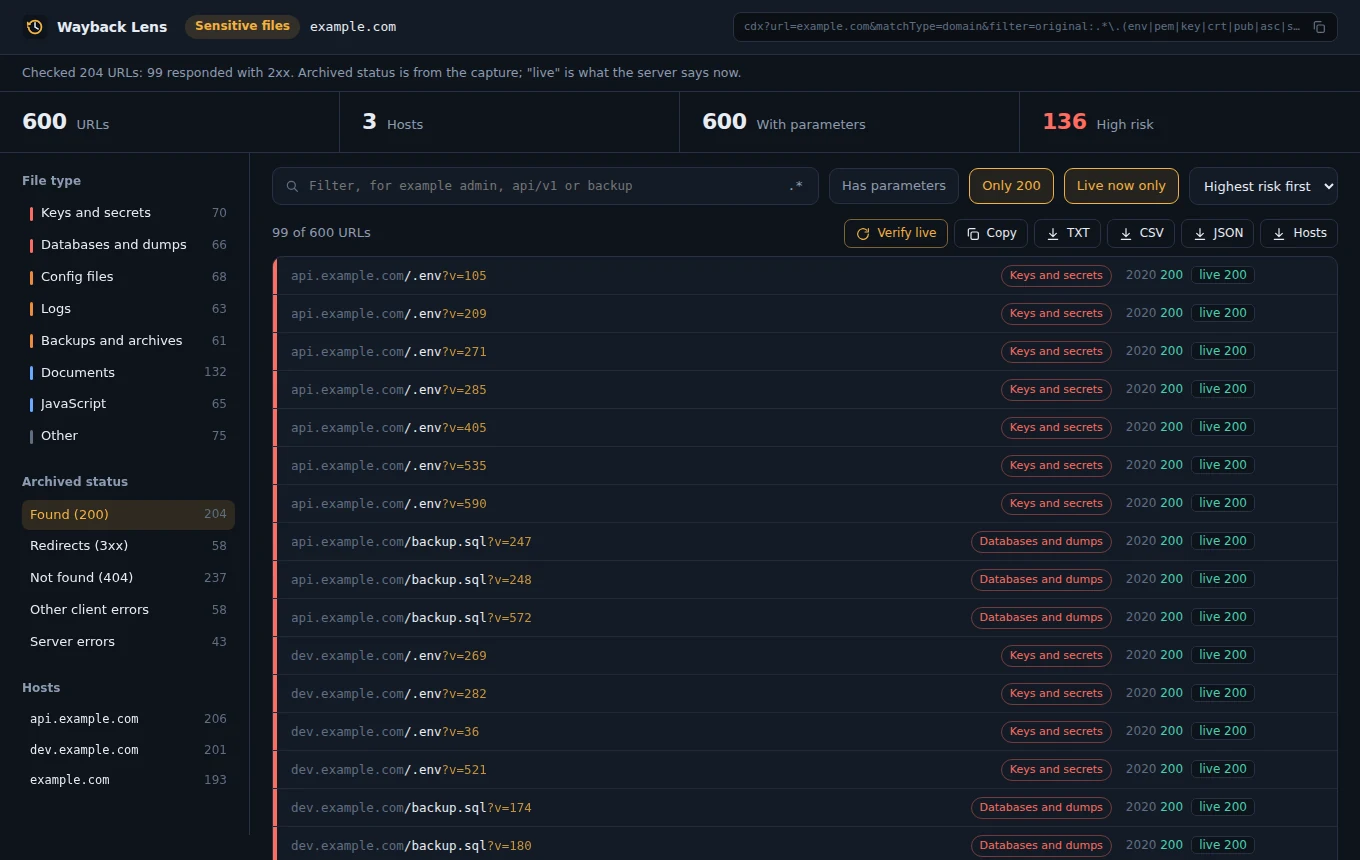
Wayback Machine CDX reconnaissance workspace for Chrome (MV3). Stream historical endpoints, rank by security risk, verify live 200s, and export triage targets.

Experience & Education

Industry penetration testing experience, law enforcement cybercrime investigations, and academic training.

Cyber Crime Intern

Jan 2026 – May 2026
Cyber Police Station, Nashik Police Commissionerate

Investigated 15+ live cybercrime and digital fraud cases adhering strictly to legal Chain of Custody procedures. Conducted deep packet-level network traffic analysis using Wireshark, OSINT threat attribution, CDR/IPDR telecom intelligence correlation, and static triage of malicious Android APKs to isolate Indicators of Compromise (IOCs).

Offensive Security Tool Architect & Researcher

2025 – Present
Independent Offensive Security Lab • AUTHENTIX Enterprise & BlindStrike

Architected AUTHENTIX Enterprise, a native Java 17/21 PortSwigger Montoya Burp Suite extension automating token lifecycle modeling, JWT tampering (alg: none, HMAC/RSA key confusion), and OAuth2 privilege escalation. Built BlindStrike, an automated blind SQL injection engine utilizing Interquartile Range (IQR) statistical latency filtering. Conducted manual Web VAPT and REST API assessments strictly aligned with OWASP Top 10 and WSTG v4.2.

B.Tech in CSE (Cyber Security & Forensics)

2023 – 2027
Sandip University, Nashik • CGPA: 7.42 / 10

Specialized coursework covering Secure Software Development Lifecycle (SSDLC), Web & Network Penetration Testing, Cryptography, Reverse Engineering, Digital Forensics, and Linux Operating System Internals. CGPA: 7.42 / 10.

Professional Certifications

Industry Credentials
EC-Council • Cisco Networking Academy
CEH v13 Badge
• Certified Ethical Hacker (CEH v13) — EC-Council Verified
• Cisco Certified Network Associate (CCNA) — Cisco Academy

• Certified Ethical Hacker (CEH v13) — EC-Council
• Cisco Certified Network Associate (CCNA) — Cisco Networking Academy
• Focus Areas: Network Defense, Web Application Attacks, Threat Intelligence, and Enterprise Penetration Testing Methodologies.

Let's Connect

Have a security inquiry, vulnerability assessment project, or full-time VAPT role to discuss? Drop a message below.

OPEN FOR FULL-TIME VAPT ROLES

Direct Contact & Roles

Available for full-time Penetration Tester and VAPT Engineer roles with immediate onboarding. Open to vulnerability assessments, AppSec engagements, and enterprise security discussions.

DIRECT PHONE / WHATSAPP
+91 87999 81052
LOCATION & MOBILITY
Pune, Maharashtra, India (Open to Relocation)

Send an Inquiry

Have a project scope, VAPT engagement, or full-time opportunity to discuss? Fill out the form below to get in touch.

Official Certificate Verification
Certificate
Candidate: Pratik Sanjay Khairnar Download High-Res Scan